GlobalWafers established its Information Security Committee in March 2023. The committee members are comprised of the highest-ranking information or information security officers from the company’s subsidiaries. Since its inception, the committee has convened biannually, but starting from December 2024, meetings will be held quarterly. The committee aims to coordinate the formulation, implementation, risk management, and compliance of policies related to information security.
To integrate information security management policies and risk management into daily operations, the company also requires each subsidiary within the group to establish its own Information Security Task Force. Members of these task forces are representatives from various departments, who discuss and communicate information security matters relevant to their departmental operations during meetings. They are responsible for implementing the information security policies and practices set forth by the Information Security Committee.
Additionally, the company incorporates information security into performance evaluations. The Information Security Office at GlobalWafers headquarters tracks the performance indicators of information security implementation at all group locations on a monthly basis. Based on operational needs, it provides information security goals, improvement guidelines, and necessary resource support to help achieve the group’s overall information security objectives. Departments are also required to implement the resolutions of the Information Security Committee, share experiences in improving information security, establish a group-wide joint defense mechanism, and enhance the overall information security framework.
Information Security Management Policy
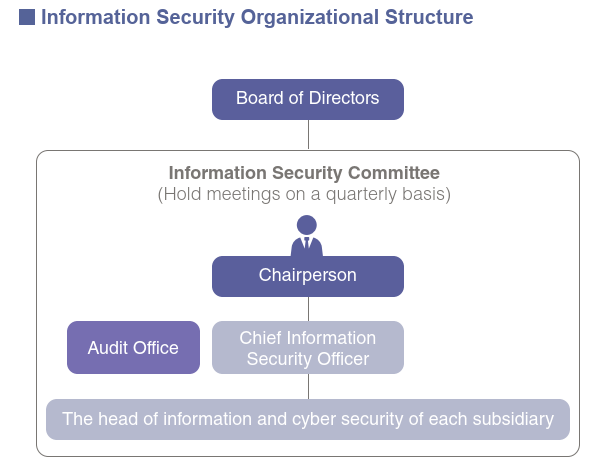
GlobalWafers has established a Chief Information Security Officer (CISO) and an information security organization to lead the execution of the company’s information security operations and the effectiveness of information security risk management mechanisms. At least once a year, the CISO reports the effectiveness of information security management and the strategic direction of information security to the Board of Directors. The overall information security management organization and the execution effectiveness of related information security operations and systems are supervised by Chairperson Hsiu-Lan Hsu, who has a background in computer science. These are regularly reviewed and revised.
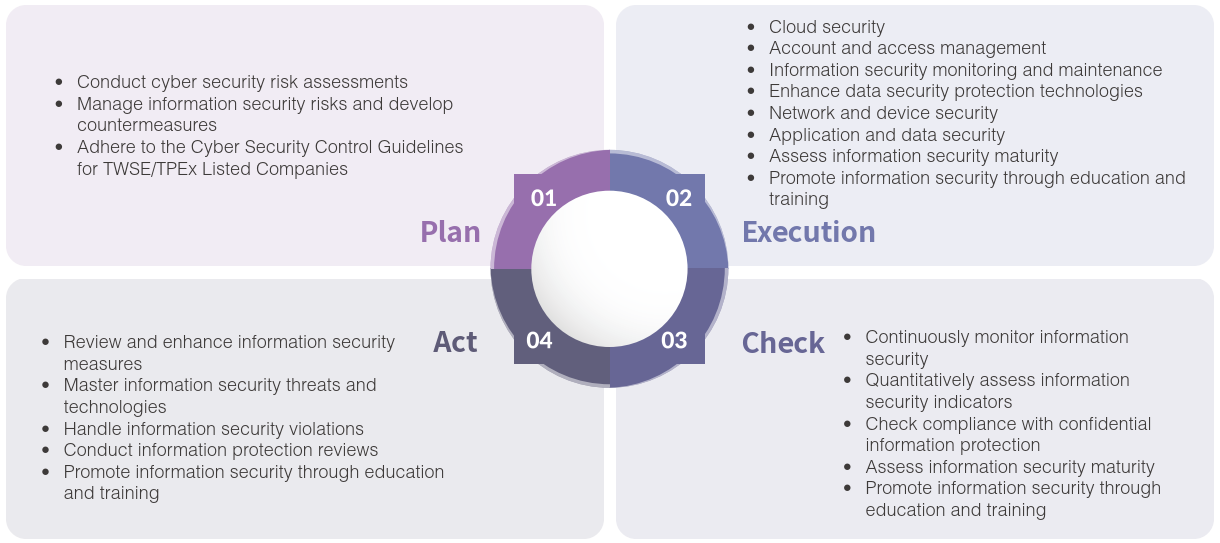
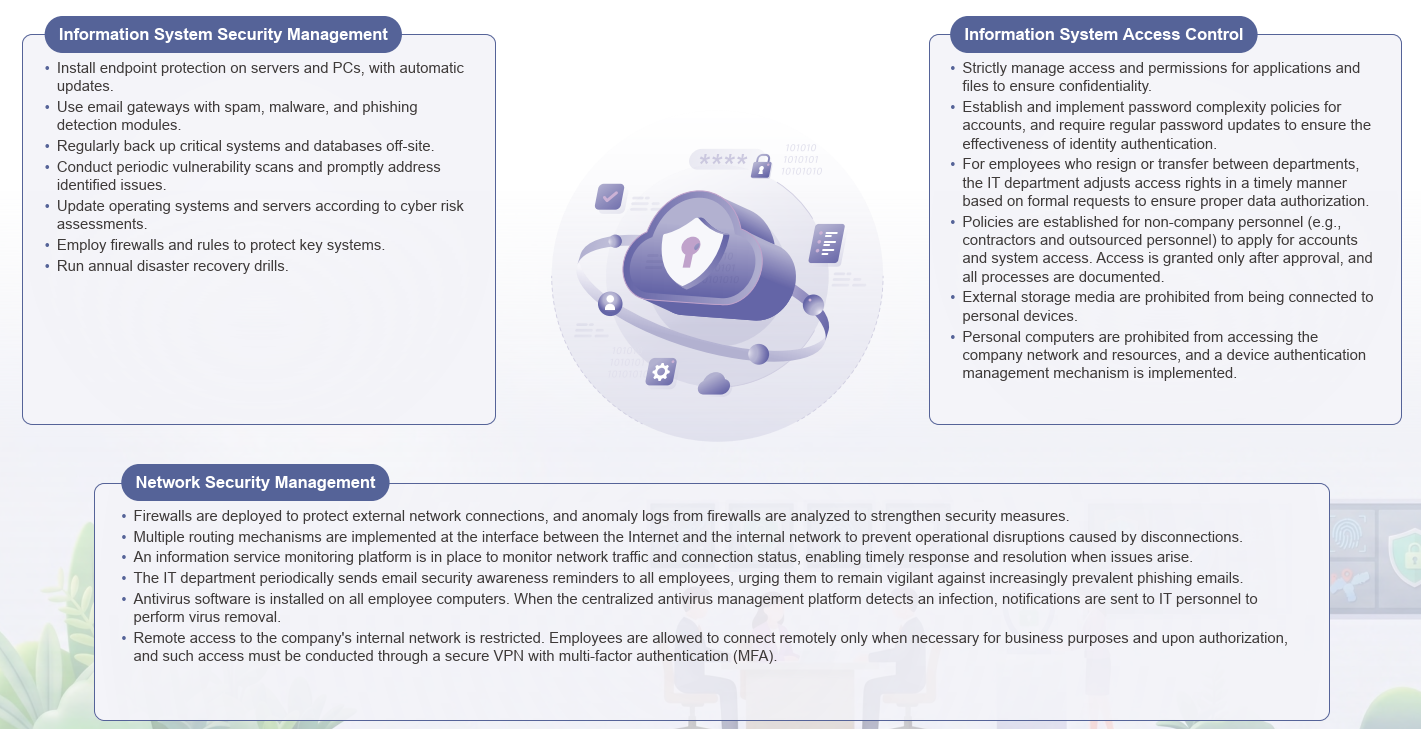
GlobalWafers takes “Information Security Governance” as the theme of the information security strategy – pursuit in compliance with the Information Security Policy, with timely introduction of new technologies for the improvement of the capacity in security information governance. “Compliance” – the Company reviews newly enacted legal rules and regulations and introduces new technology products for enhancing information security management. “Application of Technology” – cooperation with famous professional information security service provider to make improvement of information security governance capacity in these 3 aspects. Through close cooperation and mutual support, and endless improvement, the Company optimizes its capacity in overall information security defense. The Company has adopted the PDCA cycle operation model to achieve the objectives and provide continuous improvement, established information security monitoring and vulnerability scanning systems to prevent external hacker intrusions and internal secret theft, and implemented strict software and hardware control (including Internet and personal information equipment) to ensure personal data and internal confidential data protection and security.
GlobalWafers is committed to the responsible, safe, trustworthy, fair, and human-centered development and use of artificial intelligence (AI). In 2026, GlobalWafers adopted its AI Use and Security Management Guidelines, which were approved by the Chief Executive Officer. The Guidelines establish governance mechanisms—including risk classification, data protection, human review, bias prevention, record retention, auditing, and continuous monitoring—to ensure that AI is used appropriately, that risks remain under control, and that purposes, roles, and responsibilities are clearly defined.
For AI applications that may have a significant impact or present a higher level of risk, the Company will provide, in proportion to the level of risk, appropriate information about their intended purposes, scope of application, limitations, and potential risks, thereby enhancing transparency and trust throughout the AI lifecycle. Such applications must also undergo appropriate risk assessment, review, and approval before use. Their outputs must be reviewed by duly authorized personnel and must not replace professional human judgment. The relevant business units and responsible personnel retain ultimate accountability for the use of AI-generated outputs and for the resulting decisions and outcomes.
GlobalWafers is committed to protecting personal data, confidential information, and intellectual property and to complying with applicable laws and regulations. AI applications must use approved tools and environments. Input and output data associated with AI applications must be properly managed in accordance with data classification, risk classification, purpose limitation, and the principle of minimum necessary disclosure. AI must not be used for purposes that violate laws, regulations, or company policies or that may result in bias, discrimination, unfair outcomes, or harm to the rights and interests of individuals or other stakeholders. GlobalWafers also evaluates the licensing terms, privacy protections, information security measures, and governance practices of third-party service providers and suppliers, while taking energy efficiency and environmental impacts into account. Through these efforts, the Company continues to advance responsible AI applications that balance operational benefits, risk management, and sustainable development.
From 2025 to 2026, GlobalWafers conducted a total of nine AI training courses and six cross-functional AI study-group sessions. Covering topics such as data protection, enterprise applications, and AI assistants, these programs brought together representatives from various departments to strengthen their AI capabilities and knowledge through cross-functional learning and collaboration.
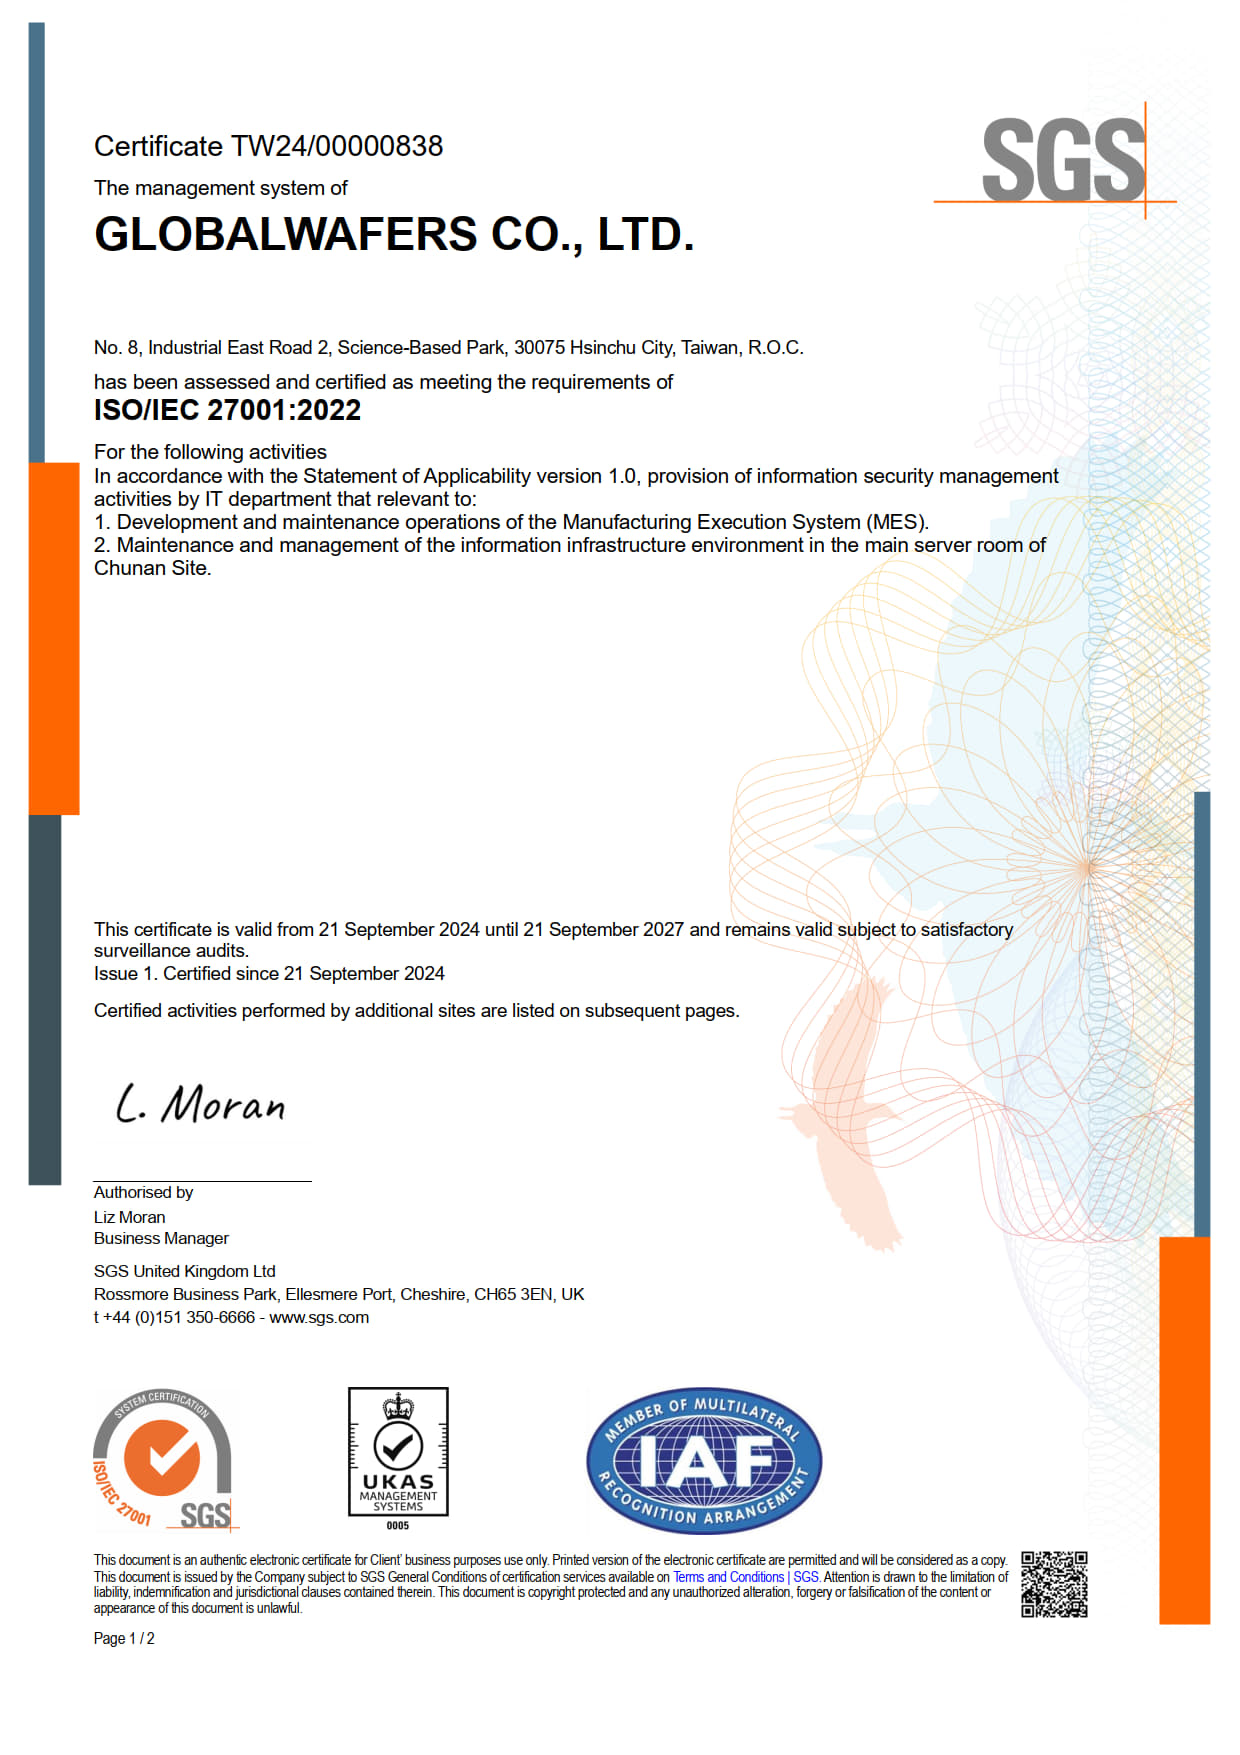
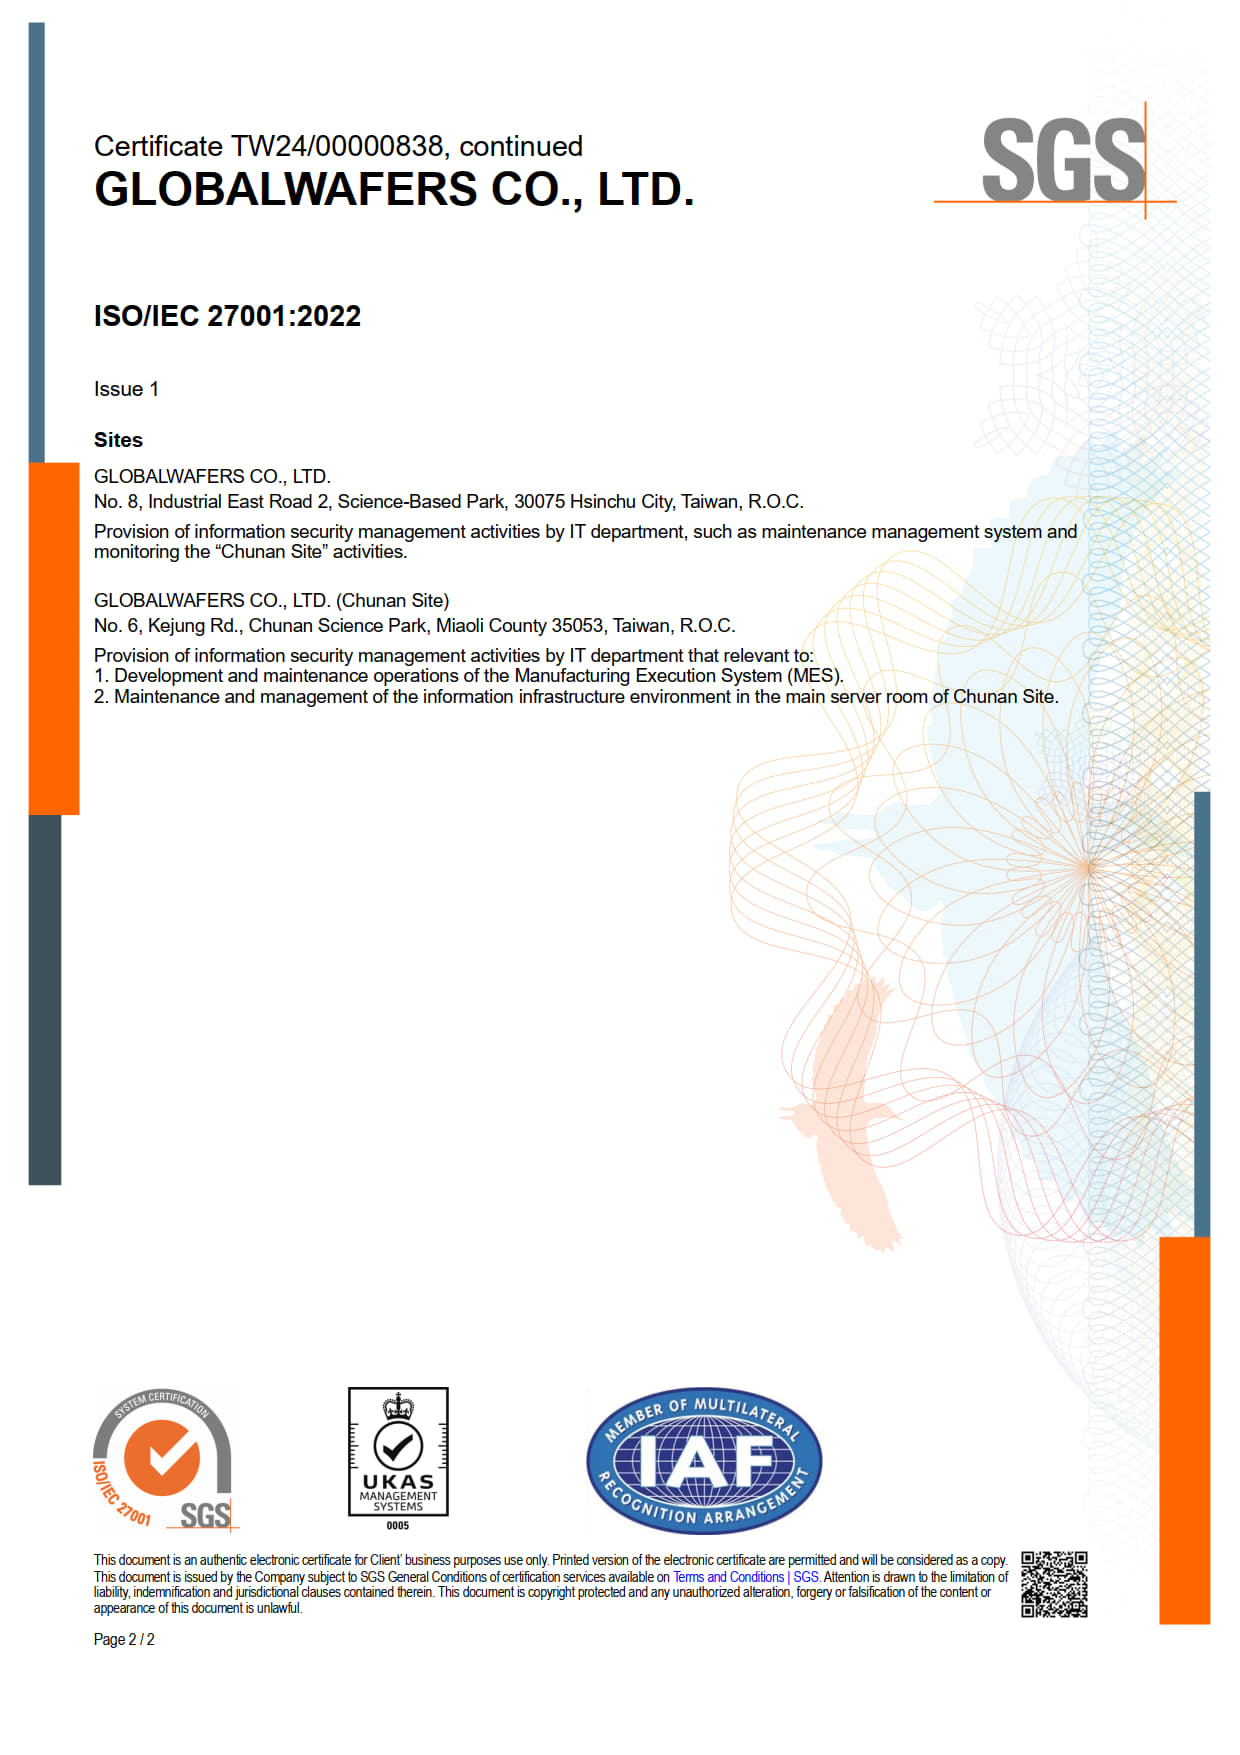
GlobalWafers has implemented the ISO 27001 Information Security Management System in 2024 and obtained ISO 27001 certification. The certification is valid from September 21, 2024, to September 21, 2027. Through the adoption of the ISO 27001 Information Security Management System, we have strengthened our ability to respond to information security incidents and ensured the protection of both our assets and those of our customers.
To prevent fraud from impersonating the staff of GlobalWafers Co., Ltd. (“GWC”), of any financial institutions, or other identities in order to commit fraud, GWC hereby reminds you that our staff will never ask you to use an ATM, remit money, provide personal information, and/or make calls to / call back any suspicious number. GWC’s staff will not ask financial institutions to give you the above instructions on our behalf.
Because the caller ID can be faked, if you receive any call that the caller ID is GWC or its number starts with “+”, “+03” or “+886”, or the caller’s statement, instruction or accent is weird, please hang it up and directly contact our staff(Human Resources Department / Mr. Chen 03-5791213), and we also encourage you to call 165 anti-fraud hotline in order to protect your lawful rights.